The Caesar cipher
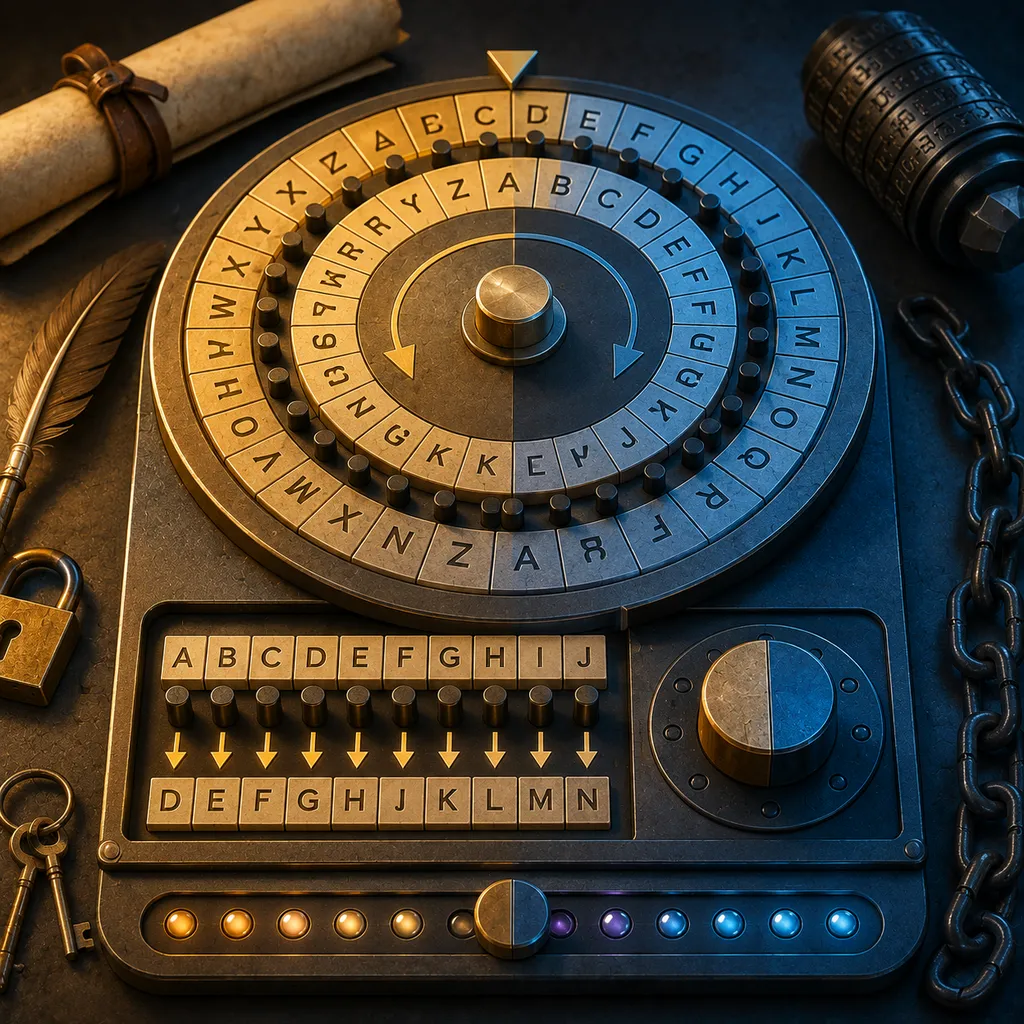
The Caesar cipher shifts each letter by k positions in the alphabet. Change the shift and see why such a small key space makes it easy to break.
I’ll give you a letter and a shift k — give its ciphertext. c = (x + k) mod 26 (A = 0 … Z = 25).
What just happened?
We replace each letter with the letter positions away in the alphabet. The bottom strip is simply the alphabet rotated by — which is why it “rotates” when you move the slider.
The Caesar cipher (modular arithmetic):
Number the letters: . Then encryption and decryption are addition modulo 26:
— is the number of the plaintext letter, is the key (the shift), is the number of the ciphertext letter. “mod 26” wraps the alphabet, so after we return to .
Why is it a weak cipher?
The whole secret is a single number . The shift changes nothing, so only 25 meaningful keys remain. To break the cipher by “brute force”, it is enough to check all 25 shifts and see which gives readable text.
Why you need this for the exam:
It is the simplest example that a cipher = a function on numbers, and that security depends on the size of the key space. By understanding , you practise congruences and the operation — tools from the number-theory topic.
Remember: the Caesar cipher is , and its key space has only 25 elements — trivially small, so brute-force breaking is instant.
Theory & formulas
Encryption
Each letter (numbered –) is shifted by the key :
Decryption
Weakness
There are only keys — a brute-force attack checks them all in a fraction of a second. It is a shift cipher, a special case of a substitution cipher.
Notation: number of the plaintext letter, of the ciphertext letter, the shift (the key).
Frequently asked questions
›Why is the Caesar cipher weak?
Because the key is just a shift of 1–25 — it is enough to check all 25 possibilities (brute force).
›How does the Caesar cipher work?
Letter x → (x+k) mod 26; decryption: (c−k) mod 26.
Teaching? Embed this experiment on your site.
Free widget — paste it on your school site, blog or notes. It links to the full version.